PT-2026-42626
تاريخ النشر
2026-05-11
·
تاريخ التحديث
2026-05-11
الوصف من
الدرجة
N/A
غير متوفرلا تتوفر حاليًا تقييمات أو مقاييس للخطورة. سنحدّث المعلومات المقابلة في الصفحة فور توفرها.
Summary
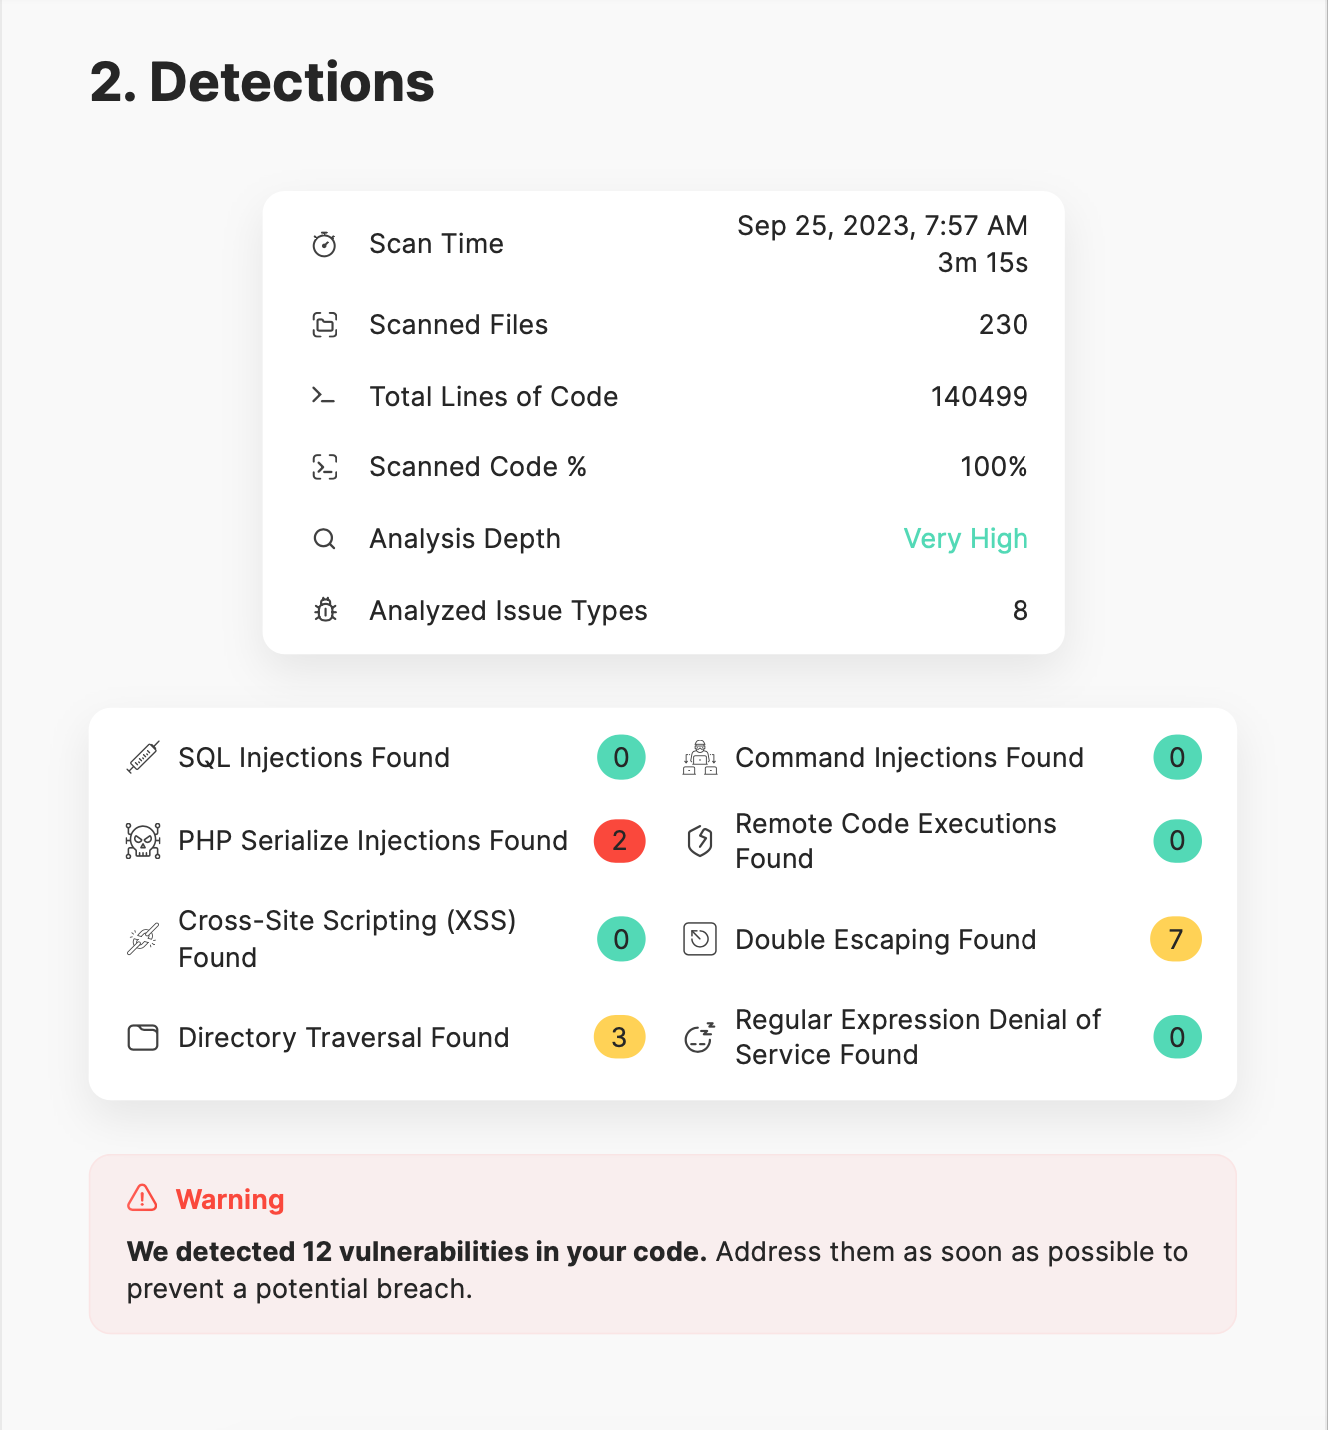
Hi, there. We've found PHP Serialize Injections in your project “torrentpier". According to the OWASP, it can pose a significant risk: enable an attacker to modify serialized objects in order to inject malicious data into the application code, resulting in code execution or an arbitrary reading of the file on any vulnerable system.
Details
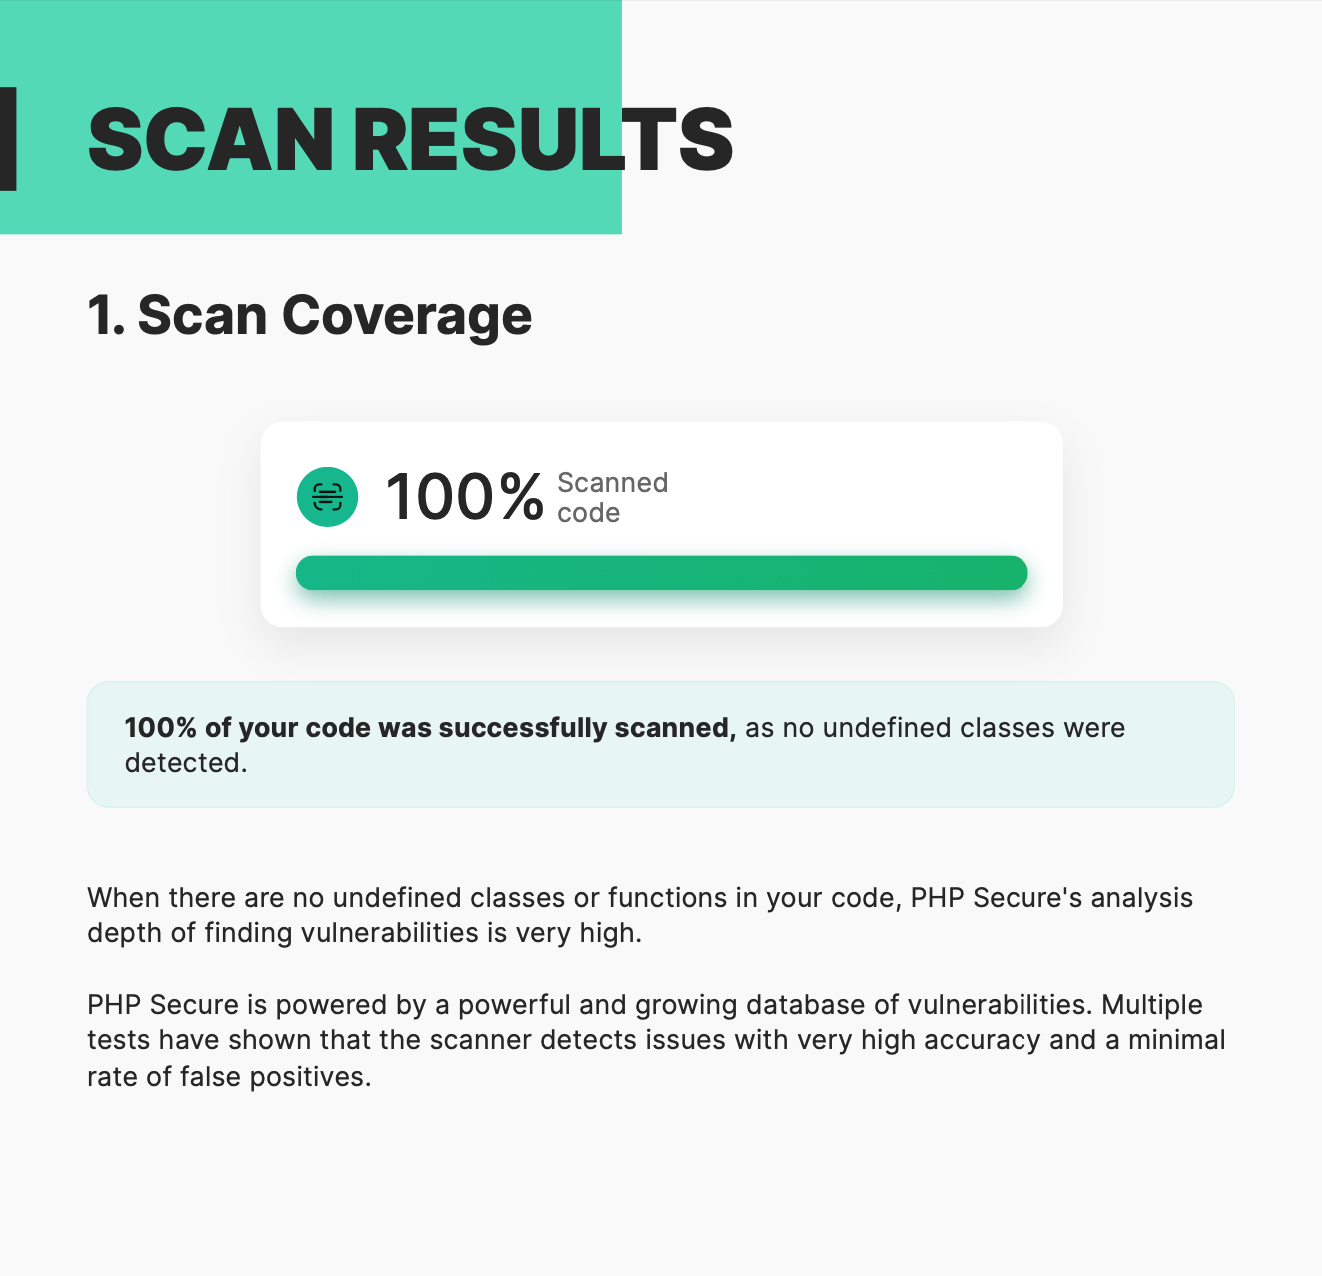
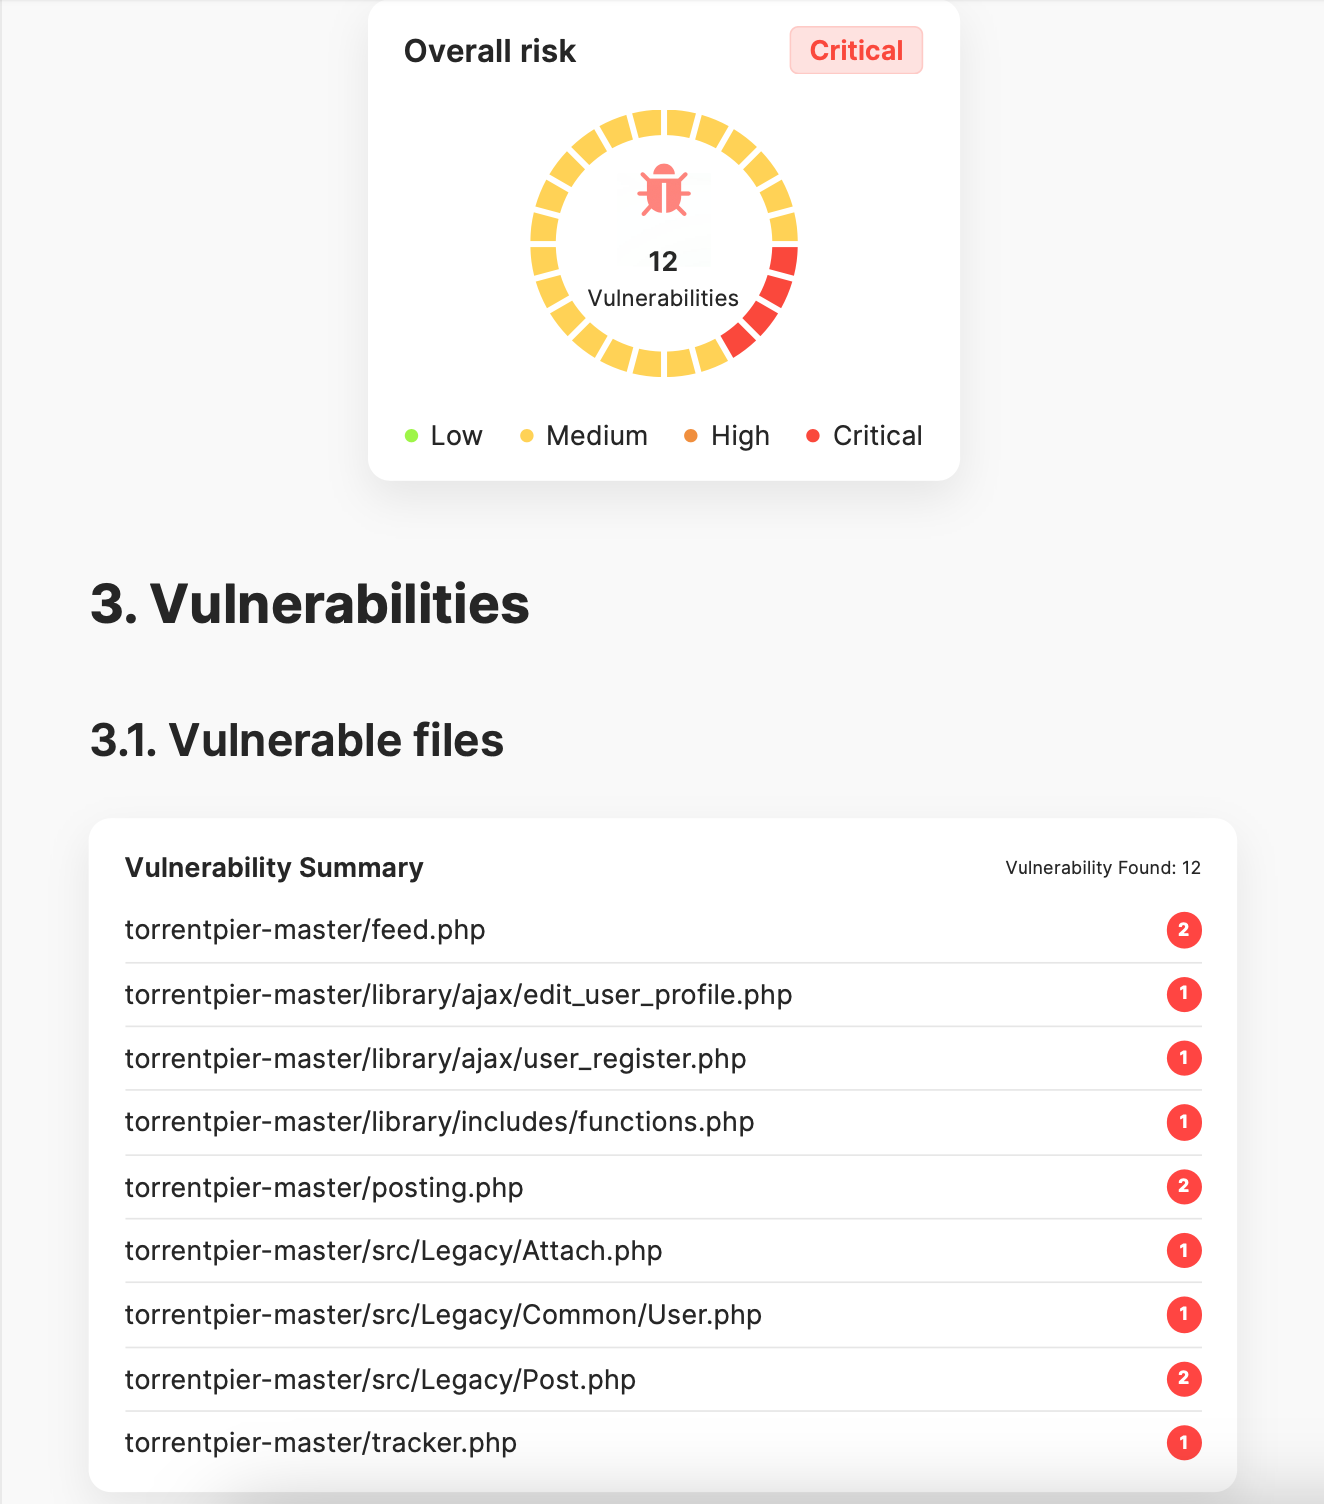
In the attachment you can find a report with the number of vulnerabilities, their types and the vulnerable files. To view the lines of vulnerable code you may scan your project with the "[PHP Secure](https://phpsecure.net/?utm source=github&utm term=torrentpier&utm content=torrentpier)" vulnerability scanner with a full access to it.
PoC
About Us
We are a team of developers of the PHP Secure vulnerability scanner. First, we checked your code automatically. Then we reviewed the vulnerable code more deeply manually and felt it was necessary to report about it to you. We suggest you scanning your code and address vulnerabilities as soon as possible to prevent a potential breach.
If you have any questions, email us at support@phpsecure.net"
وجدت خطأً في الوصف؟ لديك ما تضيفه؟ لا تتردد في مراسلتنا 👾